
范数|人工智能的梦魇:对抗攻击( 五 )
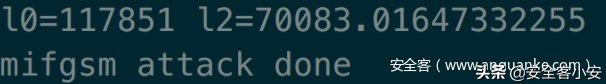
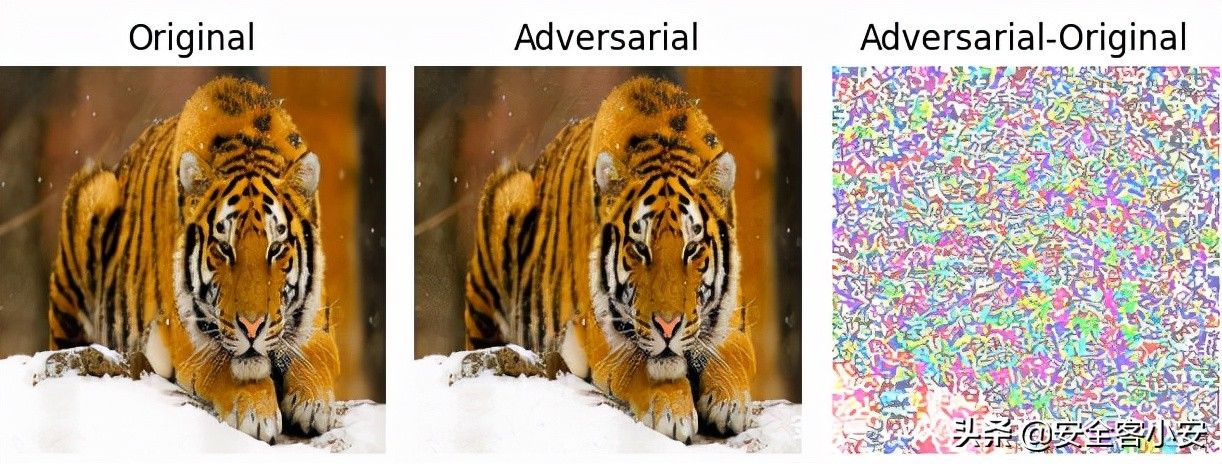
C&W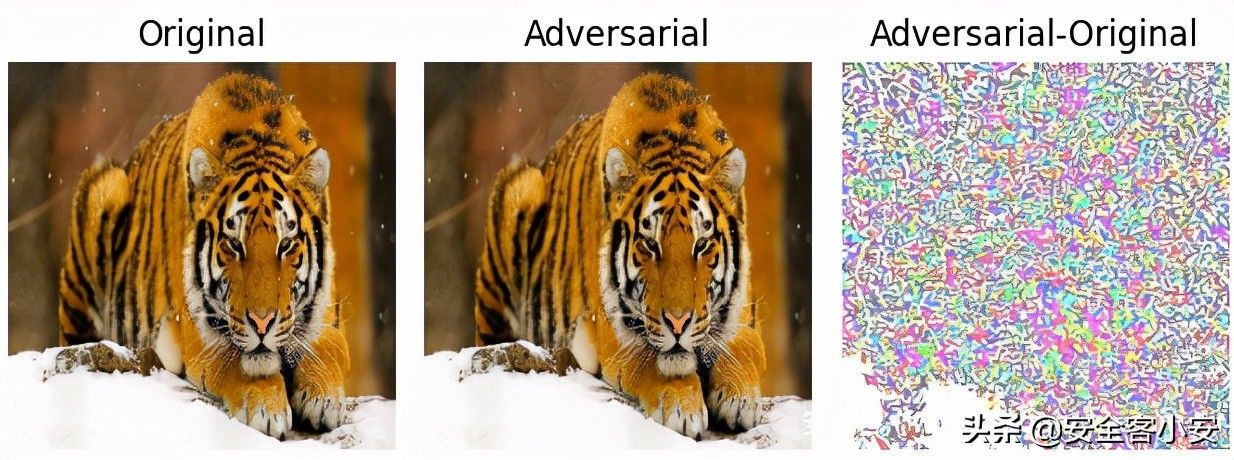
ILCM[17]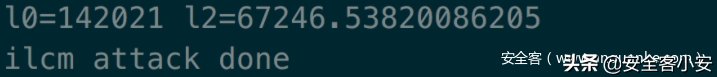
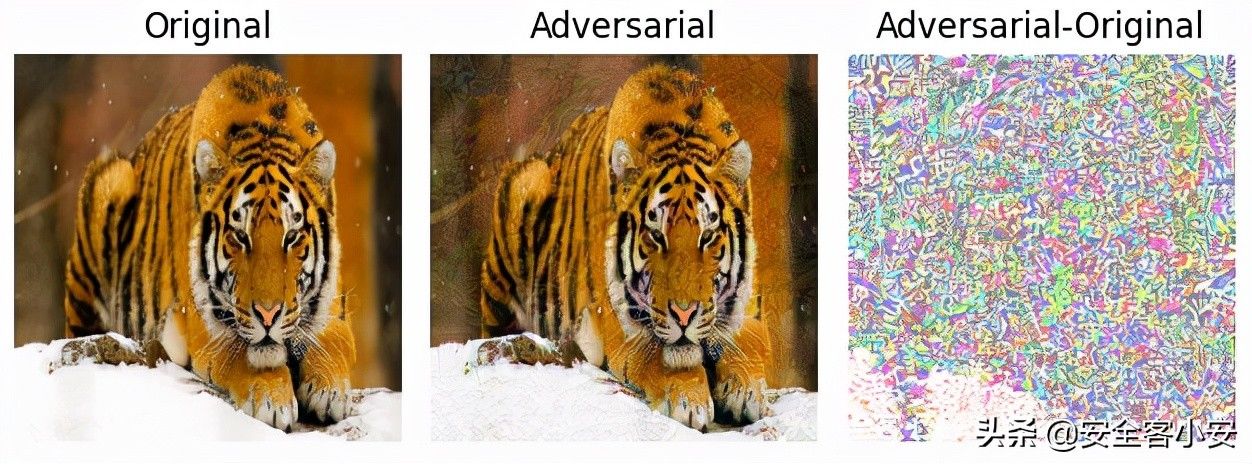
PGD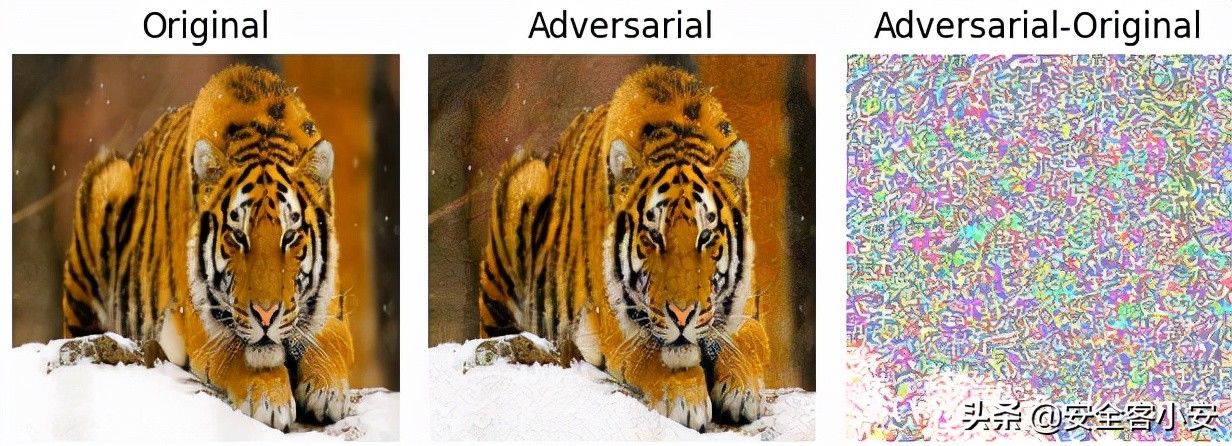
防御防御技术可以分为启发式和可证明式,启发式防御是指对某些特定攻击具有良好性能,但是没有给出防御性能的理论性保障,对抗训练就是其中的典型代表,已有的研究表明,对抗训练可以在多个数据集上抵御各种L_infiy攻击,其防御是最好的。而可证明式防御在明确知道对抗攻击类别的情况下,可证明式防御能够计算模型输出的最低精度。比如最近流行的可证明式防御是制定对抗性多面体,并通过凸松弛来限制它的上界。宽松弛过后的上界可以作为已训练模型的一个保障,它可以证明在限定的限制条件下,没有任何攻击可以超过该上界对应的攻击成功率。但是这些可证明式防御措施的实际性能仍然比对抗训练的性能差很多。相关细节不再赘述,安全客也有相关文章(“如何防御对抗攻击”)可以参考。
参考1.Intriguing properties of neural networks
2.Explaining and harnessing adversarial examples
3.Adversarial examples in the physical world
4.Boosting adversarial attacks with momentum
5.Towards evaluating the robustness of neural networks
6.The limitations of deep learning in adversarial settings
7.DeepFool: a simple and accurate method to fool deep neural networks
8.EAD: elastic-net attacks to deep neural networks via adversarial examples
9.Adversarial examples in the physical world
10.Ensemble Adversarial Training: Attacks and Defenses
11.Towards Deep Learning Models Resistant to Adversarial Attacks
12.Universal Adversarial Perturbations
13.Decision Boundary Analysis of Adversarial Exam- plesa
17.Adversarial Machine Learning at Scale
18.Spatially Transformed Adversarial Examples
19.Transferability in Machine Learning: from Phenomena to Black-Box Attacks using Adversarial Samples
20.Adversarial Spheres
21.A Closer Look at Memorization in Deep Networks
22.Practical Black-Box Attacks against Machine Learning
23.Improving Transferability of Adversarial Examples with Input Diversity
24.Adversarial transformation networks: Learning to generate adversarial examples
25.Zoo: Zeroth order optimization based black-box attacks to deep neural networks without training substitute models
本文由whoami原创发布
转载,请参考转载声明,注明出处: https://www.anquanke.com/post/id/254628【 范数|人工智能的梦魇:对抗攻击】
安全客 - 有思想的安全新媒体
- 京东|裁员不忘膈应人,这家互联网大厂送的离职礼物恶心到我了!
- iPhone14|准大学生的数码装备推荐
- 有人觉得中暑就是热出来的,吃一些退烧药就好了,这种做法 蚂蚁庄园今日答案6月28日
- 浮甘瓜于清泉,沉朱李于寒水”描述的是什么场面 蚂蚁庄园今日答案6月28日
- 个头大的车厘子比小樱桃营养价值更高,对吗 蚂蚁新村6月28日答案最新
- 位于广东省阳江市的海陵岛自然资源丰富,景色优美,该岛没有 神奇海洋6月28日答案
- 哪种水果横着切开像星星的形状 蚂蚁庄园今日答案6月29日
- 为验证人类和黑猩猩,是否会产生新的后代,科学家找来5位姑娘!
- 喜马拉雅山出现的“雪人”是何生物?目击者:智商高、攻击性强
- 为什么科学家表示人类“灭绝”的可能性极低?这些理由你赞同吗?